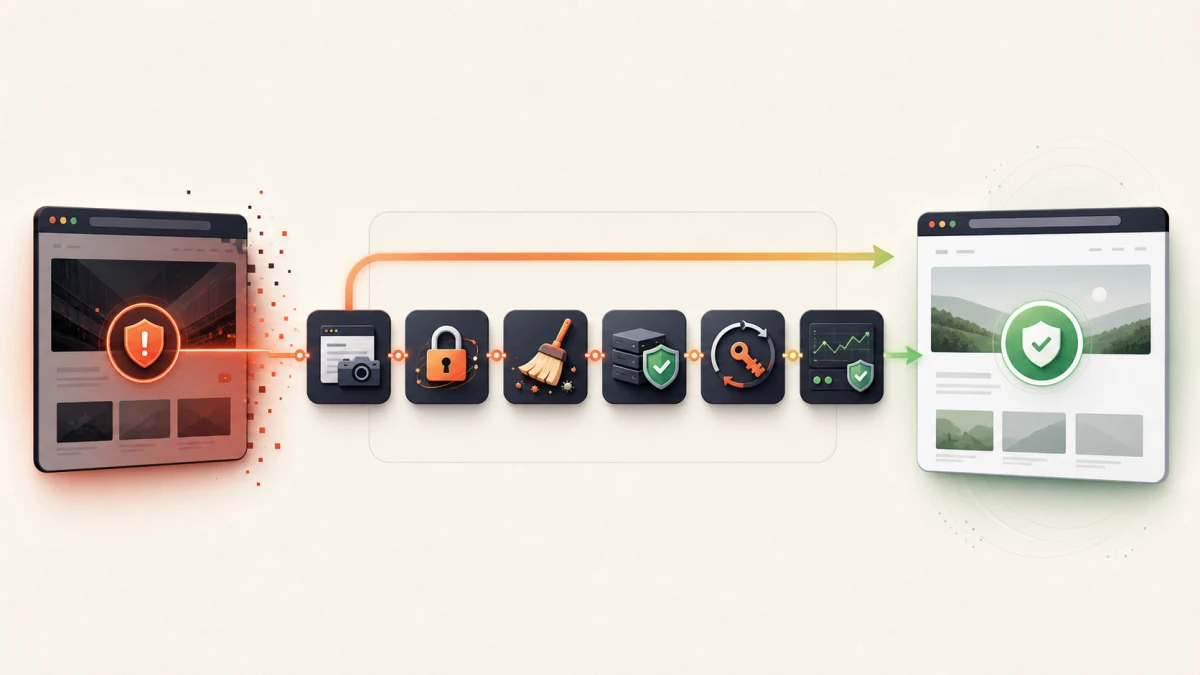
Hacked website recovery should preserve evidence, contain access, identify every affected component, remove malicious code from trusted sources, close the original entry point, rotate credentials, test the restored site, and request search-engine review only after the website is demonstrably clean.
Planning a project? Explore Crisant's website security and malware recovery service →
Begin hacked website recovery with containment
The search ‘website hacked what to do’ begins with containment, not deletion. Do not begin by deleting every suspicious file or restoring the first backup you can find. Those actions may remove evidence, overwrite clean content or return the website to a version that contains the same weakness. Record what you observed, when it began, affected URLs, warning messages, redirects, unknown users, changes made before the problem appeared. Save screenshots and ask the host to retain access and security logs.
Containment protects visitors while keeping the investigation possible. Ask the hosting provider to isolate the affected site or restrict public access using a server-level method appropriate to the stack. If payment, personal or regulated data may be involved, stop the affected workflow and follow the organisation's incident, legal and notification procedures. Do not browse known malware pages casually: Google explicitly warns that directly opening infected pages can expose the device used for investigation.
Take a snapshot of the compromised files, database, configuration and logs before cleanup when it is safe and lawful to do so. This is not the backup you will trust for restoration; it is an incident record that can help explain scope and entry point. WordPress.org likewise recommends documenting symptoms and taking an additional snapshot before cleaning. Keep that material access-controlled because it may contain malicious code, credentials or customer data.
Confirm the symptoms and establish the full scope
A hack can present as a visible defacement, an unexpected administrator, spam pages, search-result warnings, code injection, outbound email, hidden redirects or a host suspension. One symptom does not define the boundary. Check the website from administrative tools, hosting records and Search Console rather than assuming the homepage is the whole incident. Google notes that the sample URLs in its Security Issues report are examples, not necessarily a list of affected pages.
Build an inventory of the environment: domains and DNS, hosting accounts, CDN or firewall, source repository, deployment process, CMS core, themes, plugins, database, scheduled tasks, mail service, analytics tags, forms, payment integrations and administrator devices. Determine whether multiple sites share the same account or server. A neighbouring application, stolen hosting credential or vulnerable extension can widen the work beyond one WordPress directory.
Control accounts, sessions and recovery access
Assume credentials used by the affected environment may no longer be trustworthy. From a clean device, coordinate changes for hosting, registrar, DNS, CDN, CMS administrators, database users, SFTP or SSH, deployment services, email accounts and connected third parties. Remove unknown accounts, review administrator privileges and revoke active sessions or tokens where supported. Use unique passwords and multi-factor authentication, but preserve the sequence of changes in the incident record.
For WordPress, changing authentication salts invalidates existing login cookies, which helps remove sessions that should not remain active. Credentials may need a second rotation after cleanup because changing them while malicious code is still present can expose the replacements. Avoid sending passwords through ordinary chat or email. Grant the recovery team only the access it needs, store credentials in an approved password manager and remove temporary access when the incident closes.
Perform WordPress malware removal from trusted sources
WordPress malware removal must remove malicious files, injected database content, hidden administrators, backdoors and persistence mechanisms—not only the visible redirect. Replace WordPress core files with files obtained from WordPress.org, and replace themes or plugins with clean copies from their legitimate vendor or repository. Do not install software from an unofficial mirror. Preserve legitimate uploads and configuration only after reviewing them for executable code and unauthorised changes.
Inspect areas commonly abused for persistence, including must-use plugins, upload directories, theme files, server configuration, redirect rules, scheduled tasks and database options. A clean backup can accelerate recovery when its date and integrity are known, but restoring it does not explain how the attacker entered. A backup taken after the compromise may contain the malware; an older backup may remove legitimate orders, enquiries or content. Test restoration in an isolated environment before it replaces production.
Close the entry point before restoring service
A website can look clean and remain compromised. Determine the strongest evidence-supported entry point: a vulnerable or abandoned plugin, outdated core or theme, weak or reused credential, exposed administrative service, permissive file access, compromised hosting account, malicious deployment token or infected administrator device. Do not describe WordPress as unsafe merely because it is open source. The operational risk usually comes from dependencies, access, configuration, hosting and delayed maintenance.
Patch or remove the vulnerable component, update supported software, correct permissions, reduce administrator access and disable unused services. Review file editing, upload execution, API keys, database privileges, form handling and firewall rules. Apply least privilege so one stolen account cannot change everything. WordPress hardening guidance treats security as risk reduction and damage containment, not as a promise that one plugin or setting makes future compromise impossible.
Test restoration and complete the Search Console fix
Test the recovered website as a system. Verify key pages, mobile layouts, login, forms, search, checkout or payment journeys, transactional email, analytics, redirects, caching, scheduled jobs and backups. Scan externally and at the application level, review fresh logs and confirm that no unexpected outbound requests or content changes appear. Monitor closely after reopening because delayed persistence or a missed account can surface only when normal traffic returns.
If Google reported malware, code injection, deceptive content or hacked URLs, use the Security Issues report as the source of truth. Fix every listed issue across the website, not only the sample URLs, then test the work. Request a security review only after the whole site is clean. Google asks the request to explain the issue, describe the fixes and document the outcome; repeated premature submissions can delay resolution.
A ‘this site may be hacked fix’ also requires inspecting indexed pages for spam that the business did not create. Remove the generating code or unwanted content, return appropriate status codes for deleted URLs and maintain a correct sitemap. Search warnings and indexed spam may take time to update after technical recovery. Do not promise an instant removal date, and do not use ordinary URL indexing requests as a substitute for the Security Issues review process.
Turn incident recovery into continuous website care
Recovery ends when the business can operate safely and the maintenance owner can detect the next abnormal change. Establish supported core, theme and plugin versions; a review process for new extensions; least-privilege accounts; multi-factor authentication; uptime and file-integrity monitoring; protected logging; and a documented escalation path. Schedule security updates according to risk and test changes in staging when the business workflow makes that necessary.
Keep backups of files and databases, protect their integrity and test restoration rather than assuming a successful upload equals recoverability. Retention must be long enough to reach a point before a delayed compromise was introduced. Record recovery time and acceptable data loss for critical workflows, then verify that the backup schedule can meet those needs. The responsible control is a rehearsed restore, not a dashboard badge.
A search for ‘website security services Mysore’ should lead to accountable maintenance, not impossible guarantees. Review the incident without inventing certainty. Document confirmed facts, likely causes, unresolved questions, business impact, decisions and follow-up owners. Update the security runbook, remove obsolete access and schedule the next maintenance review. If you need an independent check of monitoring, backup, access and update gaps, request a free growth audit before the next release or renewal decision.
If a business website is behaving unexpectedly, start with evidence and a controlled assessment. Crisant can review the symptoms, hosting, access, backups and recovery options before cleanup decisions erase useful information or leave the original entry point open.
Request a free website security review →